The platform, on paper

Seven PDFs. No form, no sign-up, no sales call first.

Everything below is a plain A4 PDF you can forward to a colleague, attach to a procurement pack or print for a board meeting. Every screenshot is the shipped product, captured against a fictional organisation — no customer, supplier or tenant data appears in any of them.

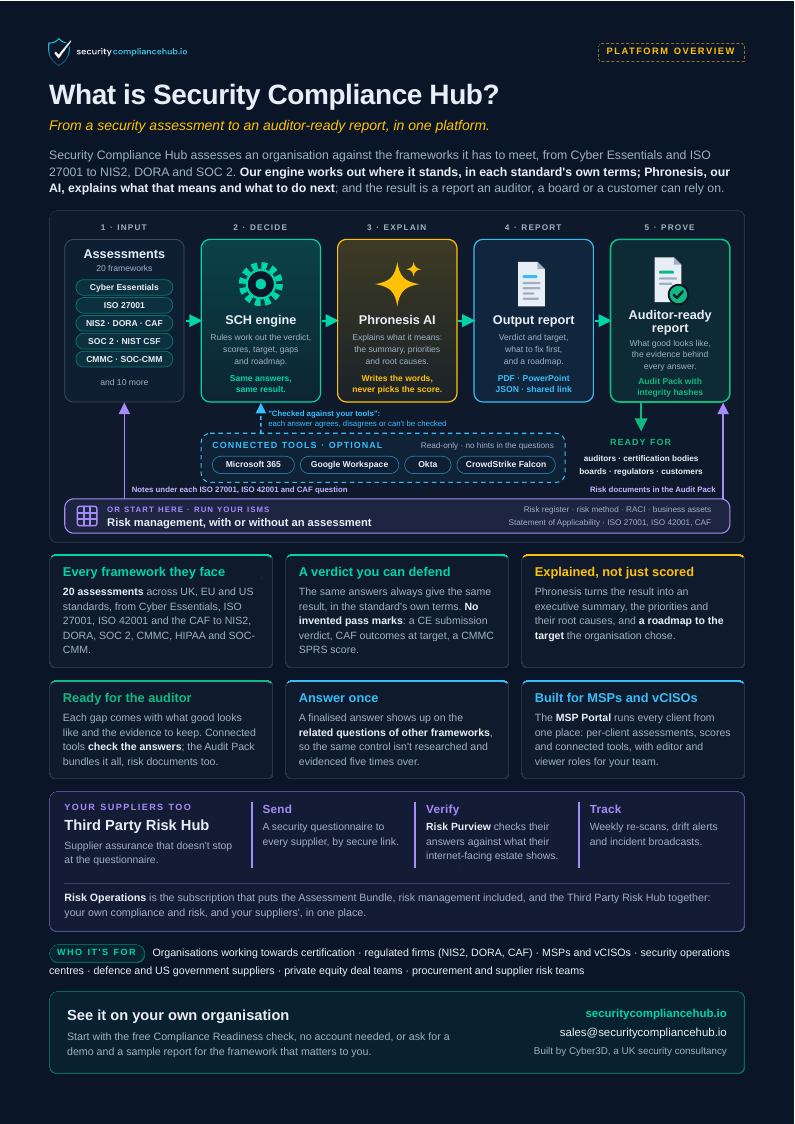
1 page The one-page overview, What is Security Compliance Hub?
Start here

What is Security Compliance Hub?

The whole platform on one page, from a security assessment to an auditor-ready report. Short enough to forward to a colleague or hand to a prospect.

  • The five steps: assessments, the SCH engine, Phronesis, your report and the Audit Pack
  • Risk management alongside them, with or without an assessment
  • Why the verdict holds up, and how your connected tools check the answers
  • The Third Party Risk Hub, Risk Operations, and who the platform is for
Download PDF
PDF · 0.2 MB
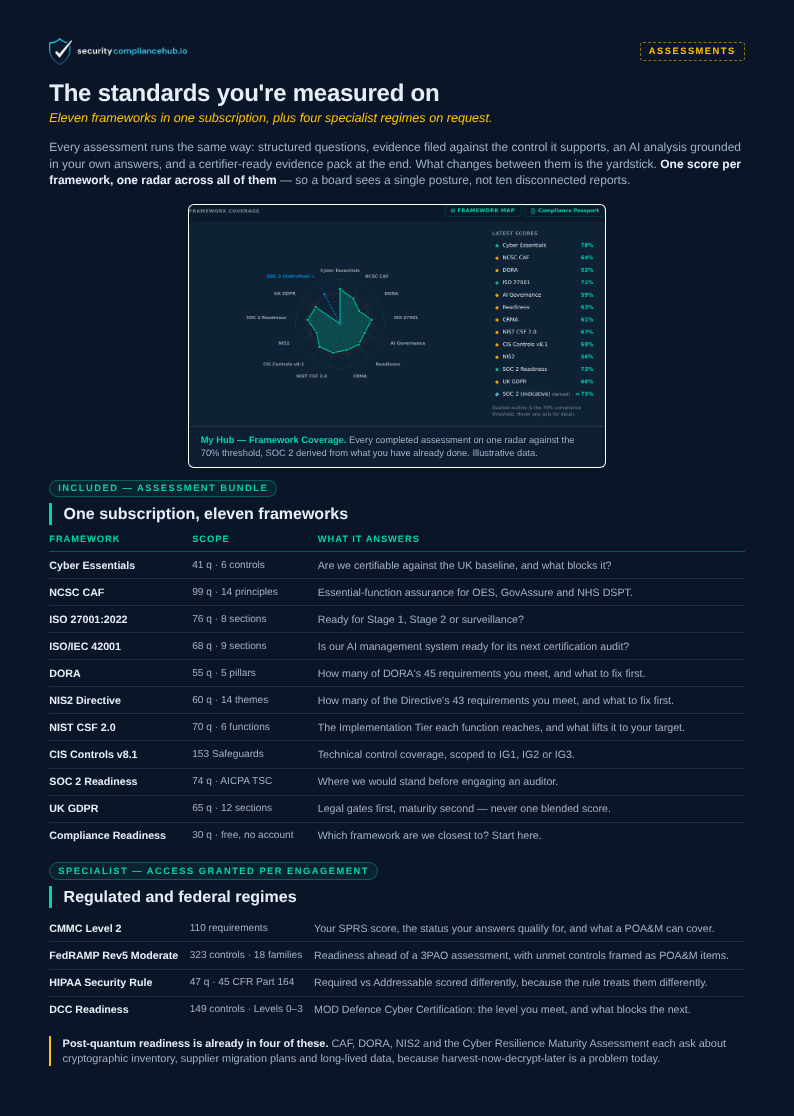
6 pages First page of the Assessment Catalogue datasheet
Frameworks

Assessment Catalogue

Every framework the Hub runs, and what each one is actually for.

  • The published standards — CE, CAF, DORA, ISO 27001, NIST CSF 2.0, CIS, NIS2, GDPR, SOC 2, CMMC, FedRAMP, HIPAA, DCC
  • The four Cyber3D-authored assessments
  • Deep dives: AI Governance, SOC Maturity (with the full SOC-CMM model), PE Cyber Due Diligence, Cyber Resilience Maturity
Download PDF
PDF · 1.1 MB
4 pages First page of the Third Party Risk Hub datasheet
Supply chain

Third Party Risk Hub

Supplier assurance that does not stop at the attestation.

  • Send — a token-gated questionnaire: 26 standard questions across 8 domains, your own, or both
  • Verify — Risk Purview scans the supplier's own domain and reports the contradictions
  • Track — weekly re-scan, drift alerts, renewals, incident comms both ways
Download PDF
PDF · 0.8 MB
4 pages First page of the problems SCH solves datasheet
The case

The Problems It Solves

Why compliance run on spreadsheets costs more than it looks — and what replaces it.

  • The cost of inconsistency, lost analyst time and evidence that decays, itemised
  • Answer a control once; every framework that asks the same thing already knows
  • Findings that become owned work, and an ISMS that outlives the assessment
Download PDF
PDF · 0.8 MB
5 pages First page of the Risk Management datasheet
ISO 27001, ISO 42001 & CAF

Risk Management

Run your risks between assessments, the way an auditor asks for them.

  • The register, reviews, your own risk method and acceptance, and a RACI approved by name
  • A Statement of Applicability pre-filled from your ISO 27001 assessment, one for each ISMS
  • Business assets in groups with owners (not an IT asset database), and eight documents for the Audit Pack
  • Supplier risks from the Third Party Risk Hub, raised from the supplier and kept current, with Risk Operations
  • An AI management system: ISO 42001's own SoA with your AI role's suggested exclusions, AI systems and impact assessments
Download PDF
PDF · 1.8 MB
3 pages First page of the Crosswalk Mapping datasheet
Crosswalks and shared gaps

Crosswalk Mapping

How the Hub links the questions of your frameworks, so work done for one shows in the others.

  • Which frameworks are linked and how closely: every pair, its links and how many are close
  • What you answered elsewhere, under the question you're answering, and where one framework asks for more
  • Across your frameworks: the gaps your frameworks share, ranked by how many frameworks one fix counts in
  • The two pairs NIST maps: CMMC with FedRAMP, and HIPAA with NIST CSF 2.0
Download PDF
PDF · 0.8 MB
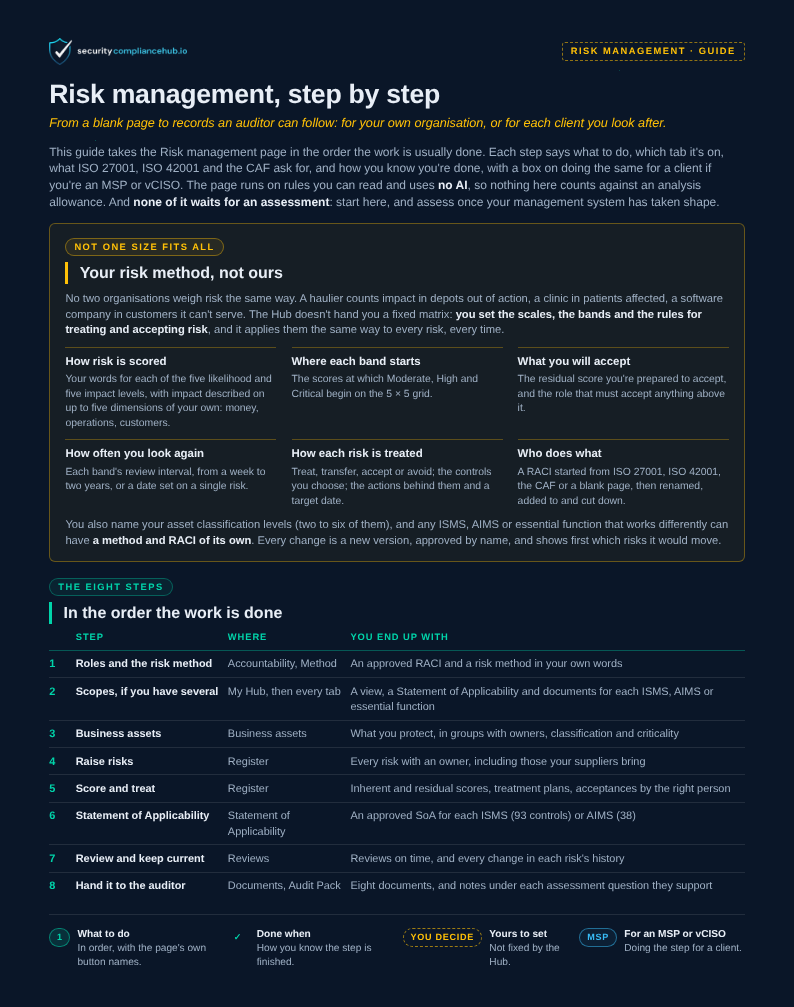
7 pages First page of Risk management, step by step
How-to guide · organisations and MSPs

Risk management, step by step

From a blank page to records an auditor can follow, in eight steps, with a box on each for an MSP or vCISO doing it for a client.

  • Your risk method, not ours: your scales and their meanings, where each band starts, what you accept and who accepts above it, how often you review
  • The RACI, scopes, business assets, raising, scoring and treating risks, the Statement of Applicability and reviews, tab by tab
  • The eight documents, the Audit Pack, and a year with the register
Download PDF
PDF · 1.8 MB
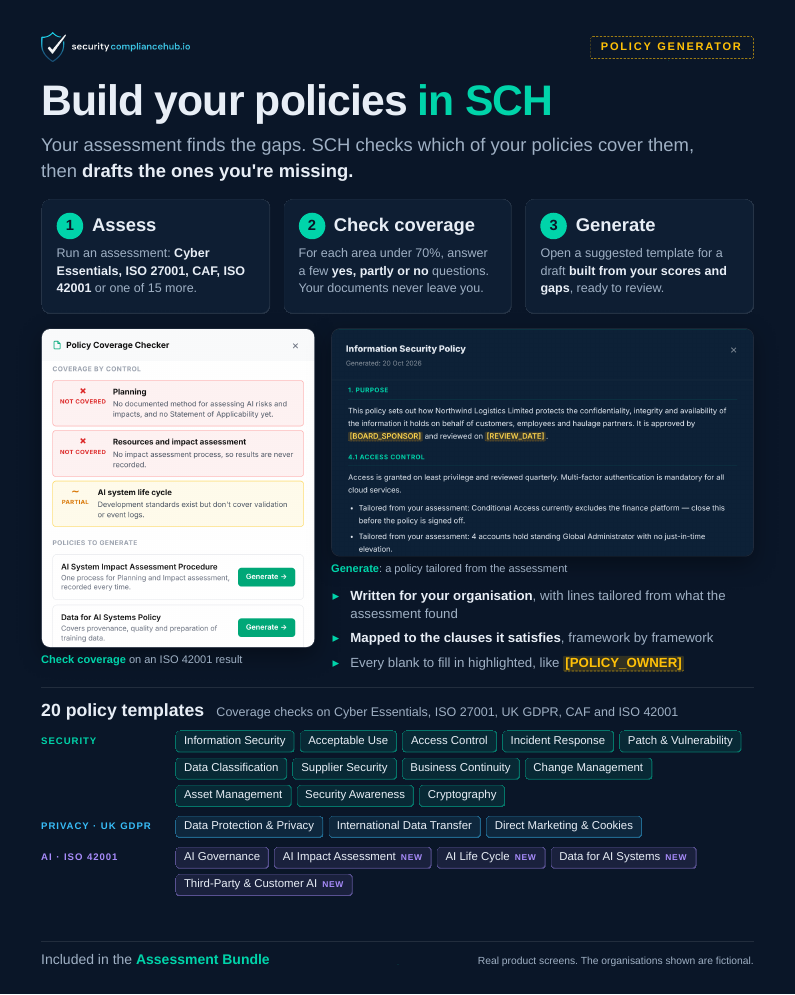
1 page Build your policies in SCH: assess, check coverage, generate
Policy Generator · one page to share

Build your policies in SCH

From the gaps your assessment finds to the policies that close them, on one page sized for LinkedIn.

  • Assess, check coverage, generate: which of your policies already cover a gap, and drafts of the ones you're missing
  • Drafts written for your organisation, mapped to the clauses they satisfy, with every blank to fill in highlighted
  • All 20 templates, from Information Security to the four for an ISO 42001 AI management system
Download PDF
PDF · 0.4 MB

Looking for a service sheet rather than a product one? These eight cover the platform itself. Consultancy engagements delivered by Cyber3D — certification readiness, gap analysis and remediation, virtual CISO, CAF assessment as a delivered service — are described on the MSP & vCISO Partner Hub, and we will send the relevant service sheet with any enquiry.

Or skip the PDF

The Compliance Readiness Assessment is free, needs no account, and gives you a cross-framework picture of where you stand in about fifteen minutes.